Map the official objectives.
Read the current Microsoft objectives and make a short list of the areas you need to revisit before booking MS-102.
MICROSOFT CERTIFICATION STUDY GUIDE
Validates skills in administering Microsoft 365 tenant-level services.
Download Revizo
Validates skills in administering Microsoft 365 tenant-level services.
Exam details are based on the available Microsoft catalogue information. Confirm current requirements with the exam provider before booking.
Use the provider's current objectives as your source of truth, then organise your Revizo sessions around the Microsoft technologies, product capabilities and implementation decisions named in the certification. The MS-102 exam is listed as Multiple choice and multiple response questions; your starting point should reflect 2+ years of Microsoft 365 administration.
Read the current Microsoft objectives and make a short list of the areas you need to revisit before booking MS-102.
Select MS-102 in Revizo and use focused question sessions to test one topic or decision type at a time, rather than relying on a single long cram session.
Use your results to return to incorrect answers, revisit the official material behind them and repeat short MS-102 practice sessions until the gaps are clearer.
FREE PRACTICE PREVIEW
Review each question, its correct answer and any available source explanation before continuing your certification study in Revizo.
Answers & available explanations
QUESTION 1
Overview -
Fabrikam, Inc. is an electronics company that produces consumer products. Fabrikam has 10,000 employees worldwide.
Fabrikam has a main office in London and branch offices in major cities in Europe, Asia, and the United States.
Existing Environment -
Active Directory Environment -
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication. Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure -
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as DNS servers.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements -
Planned Changes -
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
Project2: After the successful completion of Project1, Microsoft Teams will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft 365 bulk licenses.
Technical Requirements -
Fabrikam identifies the following technical requirements:
All users must be able to exchange email messages successfully during Project1 by using their current email address.
Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
A user named User1 must be able to view all DLP reports from the Microsoft Purview compliance portal.
Microsoft 365 Apps for enterprise applications must be installed from a network share only.
Disruptions to email access must be minimized.
Application Requirements -
Fabrikam identifies the following application requirements:
An on-premises web application named App1 must allow users to complete their expense reports online. App1 must be available to users from the My Apps portal.
The installation of feature updates for Microsoft 365 Apps for enterprise must be minimized.
Security Requirements -
Fabrikam identifies the following security requirements:
After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
The membership of the UserLicenses group must be validated monthly. Unused user accounts must be removed from the group automatically.
After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
The principle of least privilege must be used.
You are evaluating the required processes for Project1.
You need to recommend which DNS record must be created while adding a domain name for the project.
Which DNS record should you recommend?
Correct answer: C
In Question- [email protected] = username@fabrikam.com
C. text (TXT).
When you add a domain name to Microsoft 365, you’re asked to create a TXT record in DNS as a proof of domain ownership. This record won’t affect anything else in your domain. It’s only used to verify that you own the domain. After the domain is verified, you can use it with Microsoft 365 services. So, for Project1, a TXT record should be created. This will allow Microsoft 365 to verify that Fabrikam has control over the fabrikam.com DNS records.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/admin/setup/add-domain?view=o365-worldwide
QUESTION 2
Overview -
Fabrikam, Inc. is an electronics company that produces consumer products. Fabrikam has 10,000 employees worldwide.
Fabrikam has a main office in London and branch offices in major cities in Europe, Asia, and the United States.
Existing Environment -
Active Directory Environment -
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication. Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure -
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as DNS servers.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements -
Planned Changes -
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
Project2: After the successful completion of Project1, Microsoft Teams will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft 365 bulk licenses.
Technical Requirements -
Fabrikam identifies the following technical requirements:
All users must be able to exchange email messages successfully during Project1 by using their current email address.
Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
A user named User1 must be able to view all DLP reports from the Microsoft Purview compliance portal.
Microsoft 365 Apps for enterprise applications must be installed from a network share only.
Disruptions to email access must be minimized.
Application Requirements -
Fabrikam identifies the following application requirements:
An on-premises web application named App1 must allow users to complete their expense reports online. App1 must be available to users from the My Apps portal.
The installation of feature updates for Microsoft 365 Apps for enterprise must be minimized.
Security Requirements -
Fabrikam identifies the following security requirements:
After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
The membership of the UserLicenses group must be validated monthly. Unused user accounts must be removed from the group automatically.
After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
The principle of least privilege must be used.
You need to ensure that all the sales department users can authenticate successfully during Project1 and Project2.
Which authentication strategy should you implement for the pilot projects?
Correct answer: C
In Question- [email protected] = username@fabrikam.com
C: "password hash synchronization and seamless SSO."
Password Hash Synchronization: This method ensures that users can authenticate to cloud services even if the on-premises Active Directory becomes unavailable. It works by synchronizing the password hashes from your on-premises Active Directory to Azure Active Directory (Azure AD), allowing users to sign in with the same credentials they use on-premises.
Seamless Single Sign-On (SSO): Seamless SSO automatically signs users in when they are on their corporate devices connected to the corporate network. When you combine this with password hash synchronization, users benefit from a streamlined sign-in experience. They won’t need to re-enter their passwords when accessing cloud services, which minimizes disruptions to email access and other cloud-based applications.
"Users must be able to authenticate to cloud services if Active Directory becomes unavailable." That would be hash sync. Pass-though with failback is also possible but more work to implement and maintain." After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically." that's the SSO.
QUESTION 3
Overview -
Fabrikam, Inc. is an electronics company that produces consumer products. Fabrikam has 10,000 employees worldwide.
Fabrikam has a main office in London and branch offices in major cities in Europe, Asia, and the United States.
Existing Environment -
Active Directory Environment -
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication. Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure -
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as DNS servers.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements -
Planned Changes -
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
Project2: After the successful completion of Project1, Microsoft Teams will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft 365 bulk licenses.
Technical Requirements -
Fabrikam identifies the following technical requirements:
All users must be able to exchange email messages successfully during Project1 by using their current email address.
Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
A user named User1 must be able to view all DLP reports from the Microsoft Purview compliance portal.
Microsoft 365 Apps for enterprise applications must be installed from a network share only.
Disruptions to email access must be minimized.
Application Requirements -
Fabrikam identifies the following application requirements:
An on-premises web application named App1 must allow users to complete their expense reports online. App1 must be available to users from the My Apps portal.
The installation of feature updates for Microsoft 365 Apps for enterprise must be minimized.
Security Requirements -
Fabrikam identifies the following security requirements:
After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
The membership of the UserLicenses group must be validated monthly. Unused user accounts must be removed from the group automatically.
After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
The principle of least privilege must be used.
Which role should you assign to User1?
Correct answer: B
In Question- [email protected] = username@fabrikam.com
Security Reader Role: This role in Microsoft 365 allows users to view security-related features and data, including all security reports and settings in the Microsoft 365 security and compliance centers. A user assigned the Security Reader role has read-only access to the security features, making it suitable for someone who needs to view reports and audit data but does not require the ability to modify any settings or policies.
The Security Reader role in Microsoft 365 provides permissions to read security information and reports. The main task for User1 as per the scenario is to view DLP reports, and this role provides the necessary permissions for that task without granting extra, potentially unnecessary, permissions.
Reference:
https://learn.microsoft.com/en-us/purview/microsoft-365-compliance-center-permissions
QUESTION 4
HOTSPOT -
Overview -
Fabrikam, Inc. is an electronics company that produces consumer products. Fabrikam has 10,000 employees worldwide.
Fabrikam has a main office in London and branch offices in major cities in Europe, Asia, and the United States.
Existing Environment -
Active Directory Environment -
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication. Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure -
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as DNS servers.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements -
Planned Changes -
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
Project2: After the successful completion of Project1, Microsoft Teams will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft 365 bulk licenses.
Technical Requirements -
Fabrikam identifies the following technical requirements:
All users must be able to exchange email messages successfully during Project1 by using their current email address.
Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
A user named User1 must be able to view all DLP reports from the Microsoft Purview compliance portal.
Microsoft 365 Apps for enterprise applications must be installed from a network share only.
Disruptions to email access must be minimized.
Application Requirements -
Fabrikam identifies the following application requirements:
An on-premises web application named App1 must allow users to complete their expense reports online. App1 must be available to users from the My Apps portal.
The installation of feature updates for Microsoft 365 Apps for enterprise must be minimized.
Security Requirements -
Fabrikam identifies the following security requirements:
After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
The membership of the UserLicenses group must be validated monthly. Unused user accounts must be removed from the group automatically.
After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
The principle of least privilege must be used.
You create the Microsoft 365 tenant.
You implement Azure AD Connect as shown in the following exhibit.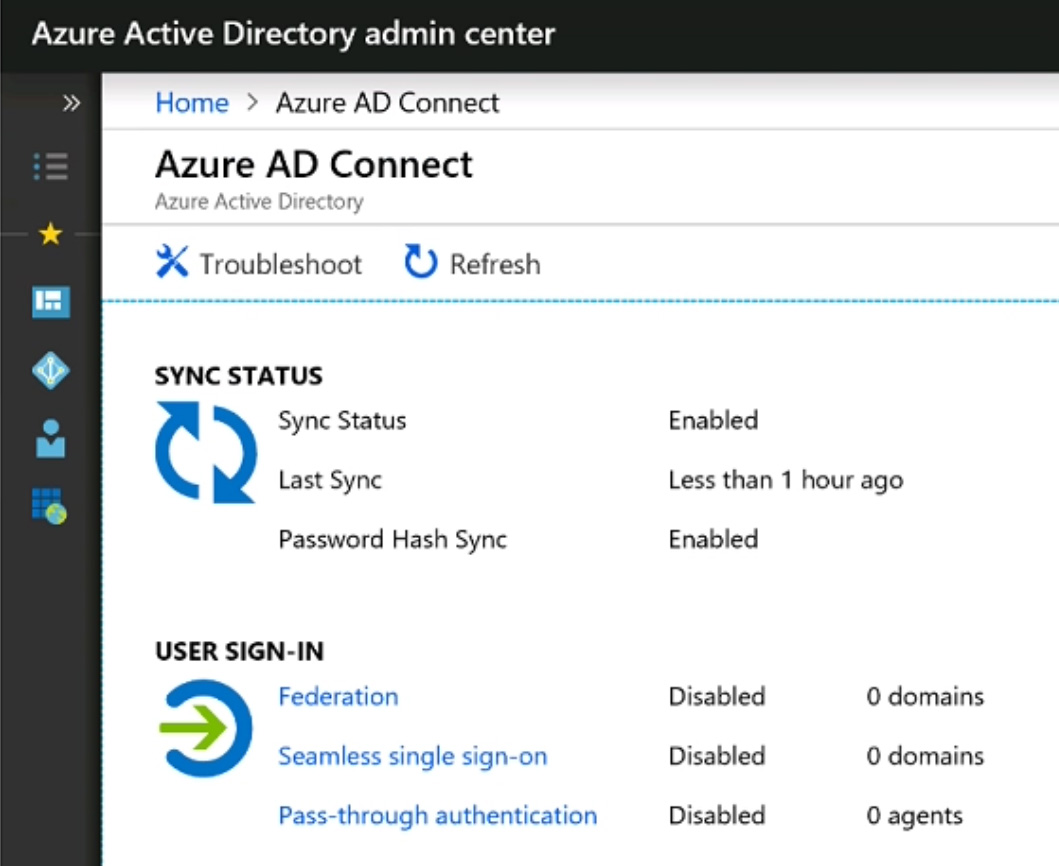
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.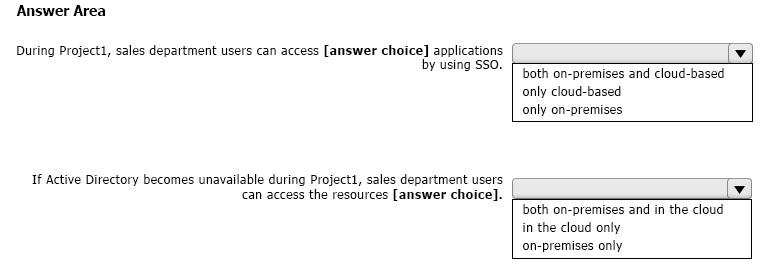
Correct answer:
In Question- [email protected] = username@fabrikam.com
1) only on-premises: no sso configured in ADConnect
2) in the cloud only: AD is not available, assuming that the on-prem app use AD to authenticate users. Exchange online is still usable because of pass hash sync.
QUESTION 5
Your company has a Microsoft 365 subscription.
You need to identify all the users in the subscription who are licensed for Office 365 through a group membership. The solution must include the name of the group used to assign the license.
What should you use?
Correct answer: C
C. the Licenses blade in the Microsoft Entra admin center**
The Licenses blade in the Microsoft Entra admin center provides detailed information on how licenses are assigned to users, including whether the assignment was done through a group membership and the name of the group responsible for the license assignment. This allows administrators to track and manage license assignments effectively.
QUESTION 6
HOTSPOT -
You have a Microsoft 365 subscription that contains the users shown in the following table.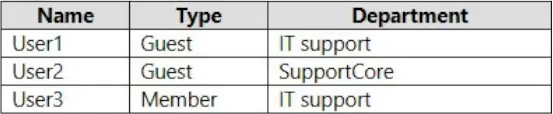
You need to configure a dynamic user group that will include the guest users in any department that contains the word Support.
How should you complete the membership rule? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.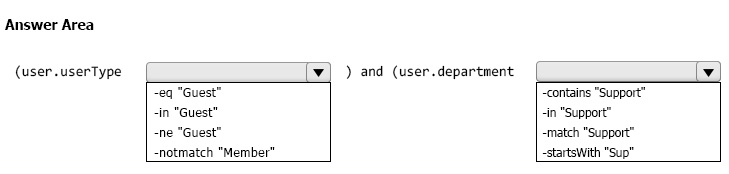
Correct answer:
(user.department -contains "Support") and (user.userType -eq "Guest")
1. user.userType =eg "Guest"
The condition -eq "Guest" is used to select users whose userType equals Guest.
This ensures that only guest users (User1 and User2) are included.
Options like -ne (not equal) or -notmatch would exclude guest users, which is not the requirement.
2. user.department -contains "Support"
The -contains "Support" condition ensures that the department includes the word Support anywhere in the string.
This is necessary as the departments "IT support" and "SupportCore" both contain the word "Support" and need to be matched.
Options like -in or -startsWith are too specific and would miss matches like "SupportCore" or "IT support."
QUESTION 7
HOTSPOT -
Your company uses a legacy on-premises LDAP directory that contains 100 users.
The company purchases a Microsoft 365 subscription.
You need to import the 100 users into Microsoft 365 by using the Microsoft 365 admin center.
Which type of file should you use and which properties are required? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.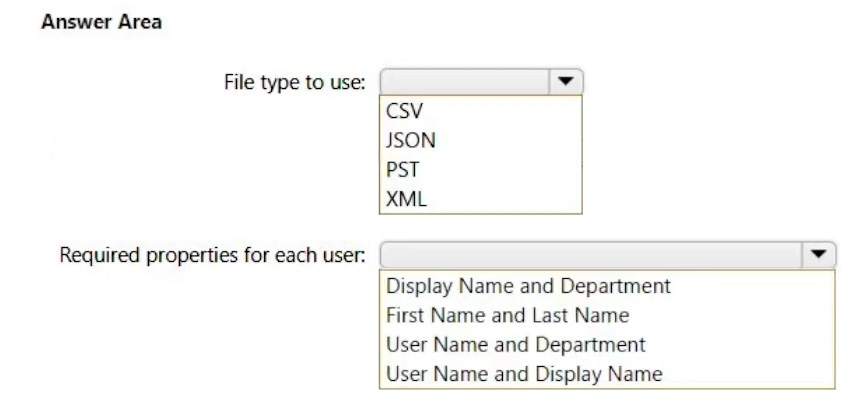
Correct answer:
File type to use: CSV
Microsoft 365 allows bulk importing of users using a CSV (Comma Separated Values) file format.
CSV is widely used because it is simple, lightweight, and compatible with most directory export tools, including legacy systems like LDAP.
Other file types like JSON, PST, or XML are not supported for bulk user imports in the Microsoft 365 Admin Center.
Required properties for each user: User Name and Display Name
Microsoft 365 requires specific mandatory properties to create user accounts:
User Name (UPN - User Principal Name): This is the email address format (e.g., user@example.com) used for sign-in.
Display Name: The name displayed for the user in directories and services.
Options like "First Name and Last Name" or "User Name and Department" may be helpful but are not the minimal required fields.
Reference:
https://learn.microsoft.com/fr-fr/training/modules/manage-accounts-licenses-microsoft-365/7-perform-bulk-user-maintenance
QUESTION 8
You have a Microsoft 365 subscription that contains the users shown in the following table.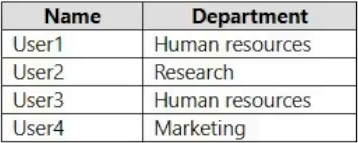
You need to configure group-based licensing to meet the following requirements:
To all users, deploy an Office 365 E3 license without the Power Automate license option.
To all users, deploy an Enterprise Mobility + Security E5 license.
To the users in the research department only, deploy a Power BI Pro license.
To the users in the marketing department only, deploy a Visio Plan 2 license.
What is the minimum number of deployment groups required?
Correct answer: C
3 groups needed : - Group 1 : All users (deploy EMS+S E5 licence and O365 E3 licence with "Power Automate for Office 365" disabled. - group 2 : "Research group" : deploy Power Bi Pro Licence (not included in O365 E3 but in O365 E5). - Group 3 : "Marketing group" deploy Visio plan 2 Licence.
QUESTION 9
You have a Microsoft 365 subscription.
You view the Service health Overview as shown in the following exhibit.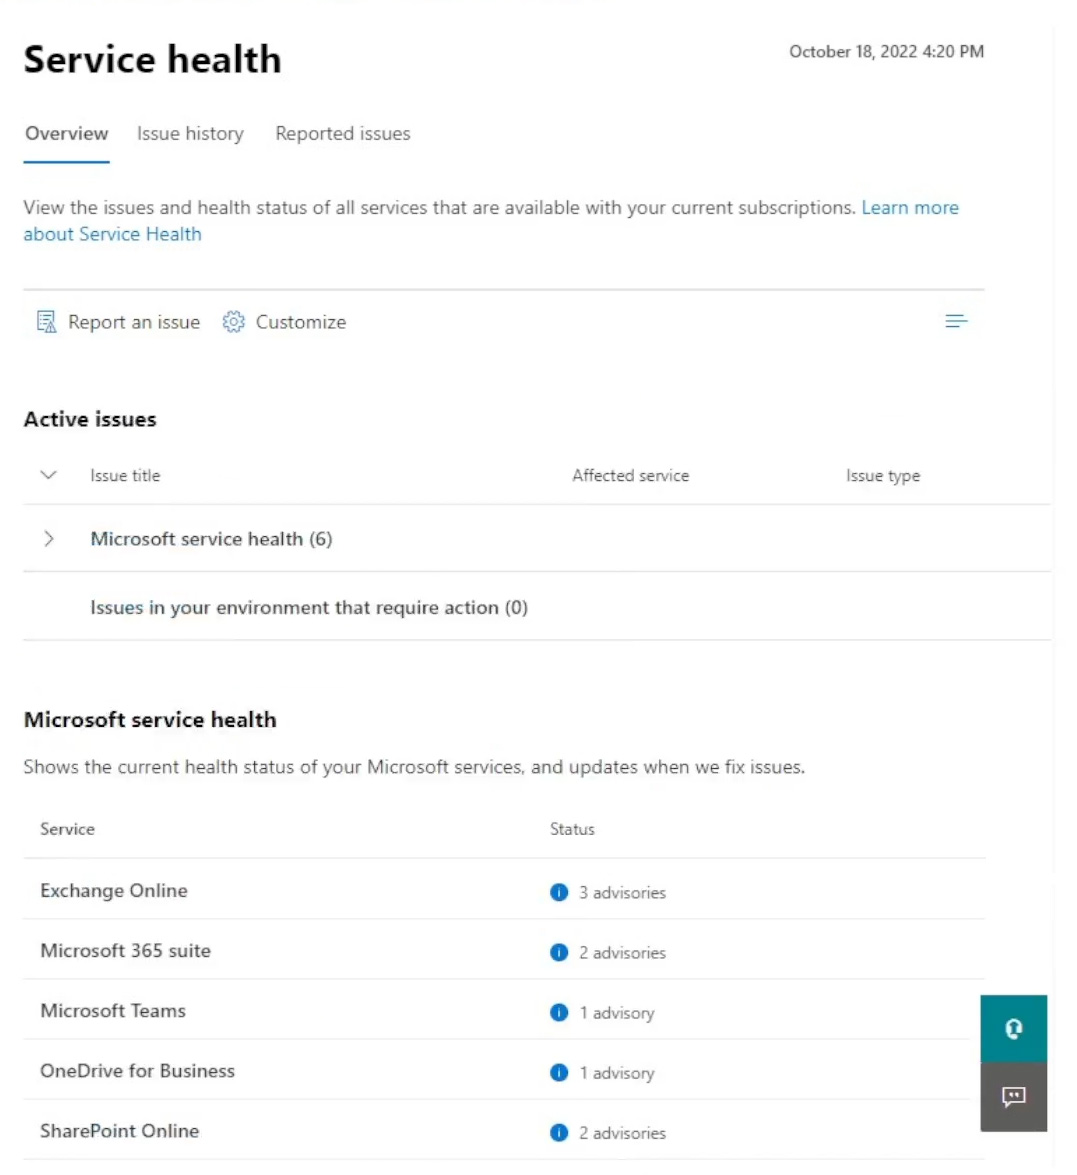
You need to ensure that a user named User1 can view the advisories to investigate service health issues.
Which role should you assign to User1?
Correct answer: C
Service Support Administrator - Assign the Service Support admin role as an additional role to admins or users who need to do the following in addition to their usual admin role:
- Open and manage service requests
- View and share message center posts
- Monitor service health
Reference:
https://learn.microsoft.com/en-us/microsoft-365/admin/add-users/about-admin-roles?view=o365-worldwide#commonly-used-microsoft-365-admin-center-roles
QUESTION 10
HOTSPOT -
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.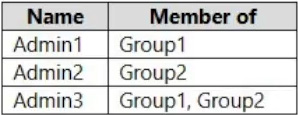
You add the following assignment for the User Administrator role:
Scope type: Directory -
Selected members: Group1 -
Assignment type: Active -
Assignment starts: Mar 15, 2023 -
Assignment ends: Aug 15, 2023 -
You add the following assignment for the Exchange Administrator role:
Scope type: Directory -
Selected members: Group2 -
Assignment type: Eligible -
Assignment starts: Jun 15, 2023 -
Assignment ends: Oct 15, 2023 -
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.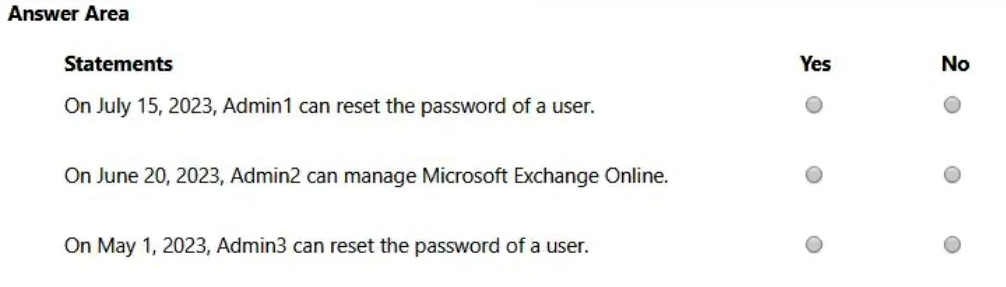
Correct answer:
Yes, Yes , Yes
On July 15, 2023, admin 1 can reset the password of a user.
Yes. Admin 1 is a member of Group 1, which has been assigned the User Administrator role actively from March 15, 2023, to August 15, 2023. This role permits password reset actions among others.
On June 20, 2023, admin 2 can manage Microsoft Exchange Online.
Yes, but with a condition. Admin 2 is a member of Group 2, which has been assigned the Exchange Administrator role as eligible from June 15, 2023, to October 15, 2023. However, since the assignment type is "Eligible," admin 2 needs to activate the role to perform the Exchange Administrator tasks. Once activated, admin 2 can manage Microsoft Exchange Online.
On May 1, 2023, admin 3 can reset the password of a user.
Yes. Admin 3 is a member of both Group 1 and Group 2. Since Group 1 has the User Administrator role assigned actively from March 15, 2023, to August 15, 2023, admin 3 can reset the password of a user during this period.
QUESTION 11
You have a Microsoft 365 subscription.
You have an Azure AD tenant that contains the users shown in the following table.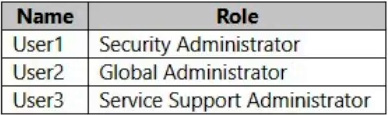
You configure Tenant properties as shown in the following exhibit.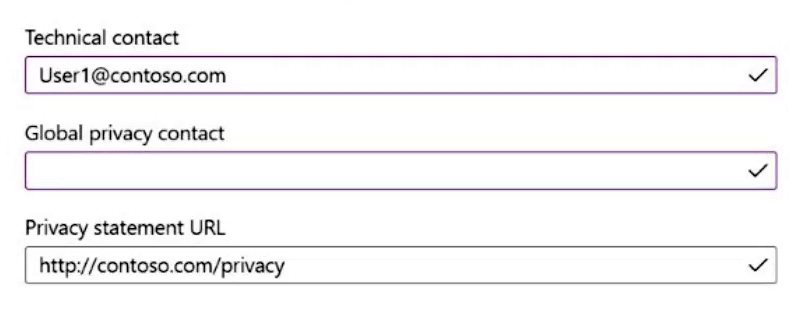
Which users will be contacted by Microsoft if the tenant experiences a data breach?
Correct answer: B
"Global privacy contact: Type the email address for the person to contact for inquiries about personal data privacy. This person is also who Microsoft contacts if there's a data breach related to Azure Active Directory services. If there's no person listed here, Microsoft contacts your Global Administrators.
Reference:
https://learn.microsoft.com/en-us/azure/active-directory/fundamentals/properties-area
QUESTION 12
Your network contains an Active Directory forest named contoso.local.
You purchase a Microsoft 365 subscription.
You plan to move to Microsoft 365 and to implement a hybrid deployment solution for the next 12 months.
You need to prepare for the planned move to Microsoft 365.
What is the best action to perform before you implement directory synchronization? More than one answer choice may achieve the goal. Select the BEST answer.
Correct answer: D
D. Purchase a custom domain name.
The best action to take before implementing directory synchronization for a hybrid deployment with Microsoft 365 would be to purchase a custom domain name. When you set up Microsoft 365, you're prompted to provide your domain name. This domain should match the domain you use within your on-premises Active Directory environment to ensure a seamless user experience and email delivery.
QUESTION 13
You have a Microsoft 365 subscription.
You configure a new Azure AD enterprise application named App1. App1 requires that a user be assigned the Reports Reader role.
Which type of group should you use to assign the Reports Reader role and to access App1?
Correct answer: C
You can not assign Azure AD roles to dynamic groups. And you don't need a mailbox/ share point /etc, so it is not a 365 group.
The correct answer is C. a security group that has assigned membership. This type of group can be used to assign users and groups to an enterprise application and to a specific app role
Option A. a Microsoft 365 group that has assigned membership is not correct because Microsoft 365 groups are not supported for app role assignment
Option B. a Microsoft 365 group that has dynamic user membership is not correct because Microsoft 365 groups are not supported for app role assignment
Option D. a security group that has dynamic user membership is not correct because security groups with dynamic membership are not supported for app role assignment.
QUESTION 14
You have a new Microsoft 365 E5 tenant.
You need to enable an alert policy that will be triggered when an elevation of Microsoft Exchange Online administrative privileges is detected.
What should you do first?
Correct answer: A
A. Enable auditing
The first step you should take is to Enable auditing.
In order to monitor and get alerted on specific activities such as elevation of administrative privileges, auditing needs to be enabled in your Microsoft 365 environment. Auditing will record events such as changes in permissions and other administrative activities, which can then be monitored through alert policies to notify administrators when specific events occur.
QUESTION 15
Your network contains an on-premises Active Directory domain named contoso.com. The domain contains 1,000 Windows 10 devices.
You perform a proof of concept (PoC) deployment of Microsoft Defender for Endpoint for 10 test devices. During the onboarding process, you configure Microsoft Defender for Endpoint-related data to be stored in the United States.
You plan to onboard all the devices to Microsoft Defender for Endpoint.
You need to store the Microsoft Defender for Endpoint data in Europe.
What should you do first?
Correct answer: D
D. Offboard the test devices.
Offboarding the test devices as a first step, followed by setting up/creating a new workspace in Europe. If the data storage location is tied to the workspace and cannot be changed once set, then it would make sense to offboard the test devices from the current workspace before creating a new workspace in the data storage location of Europe.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/security/defender-endpoint/data-storage-privacy?view=o365-worldwide
QUESTION 16
You have a Microsoft 365 E5 subscription that contains a user named User1.
User1 exceeds the default daily limit of allowed email messages and is on the Restricted entities list.
You need to remove User1 from the Restricted entities list.
What should you use?
Correct answer: D
Remove a user from the Restricted entities page in the Microsoft 365 Defender portal In the Microsoft 365 Defender portal at https://security.microsoft.com, go to Email & collaboration > Review > Restricted entities. Or, to go directly to the Restricted entities page, use https://security.microsoft.com/restrictedentities.
https://learn.microsoft.com/en-us/microsoft-365/security/office-365-security/removing-user-from-restricted-users-portal-after-spam?view=o365-worldwide
QUESTION 17
Your company has a Microsoft 365 E5 subscription.
Users in the research department work with sensitive data.
You need to prevent the research department users from accessing potentially unsafe websites by using hyperlinks embedded in email messages and documents. Users in other departments must not be restricted.
What should you do?
Correct answer: D
D. Create a new safe links policy.
With this action, you can create a Safe Links policy specifically targeting the users in the research department, ensuring that only they are restricted from accessing potentially unsafe websites through hyperlinks, while other departments remain unaffected.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/office-365-security/set-up-atp-safe-links-policies?view=o365-worldwide
QUESTION 18
HOTSPOT -
You have an Azure AD tenant that contains the users shown in the following table.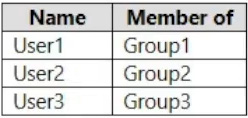
Your company uses Microsoft Defender for Endpoint. Microsoft Defender for Endpoint contains the roles shown in the following table.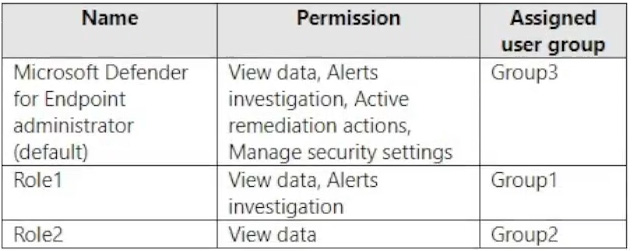
Microsoft Defender for Endpoint contains the device groups shown in the following table.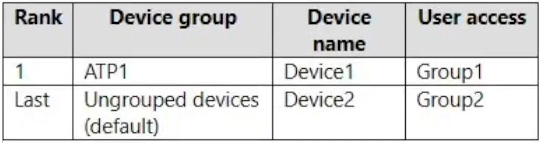
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.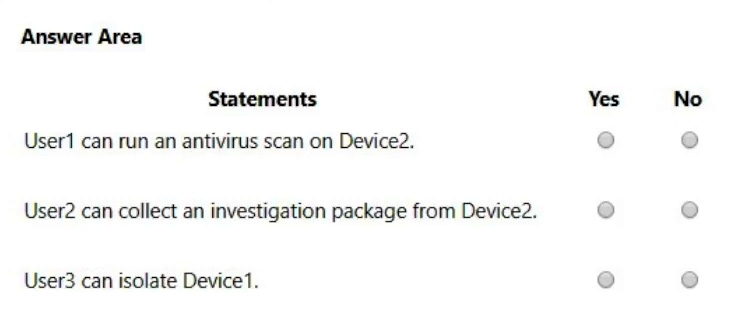
Correct answer:
User 1 can run an antivirus scan on device 2.
No. User 1 belongs to Group 1 and has the permission to "View data, alerts investigations" under role 1. Running an antivirus scan would typically require additional permissions which are not listed here for User 1.
User 2 can collect an investigation package from device 2.
No. User 2 belongs to Group 2 and has the permission to "View data" under role 2. Collecting an investigation package would likely require additional permissions which are not listed for User 2.
User 3 can isolate device 1.
Yes. User 3 belongs to Group 3 and has the role of Microsoft Defender for Endpoint Administrator which includes permissions to "View data, alerts investigations, active remediations, manage security settings." These permissions encompass the ability to take actions such as isolating a device.
QUESTION 19
HOTSPOT -
You have a Microsoft 365 E5 tenant.
You need to ensure that administrators are notified when a user receives an email message that contains malware. The solution must use the principle of least privilege.
Which type of policy should you create, and which Microsoft Purview solutions role is required to create the policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.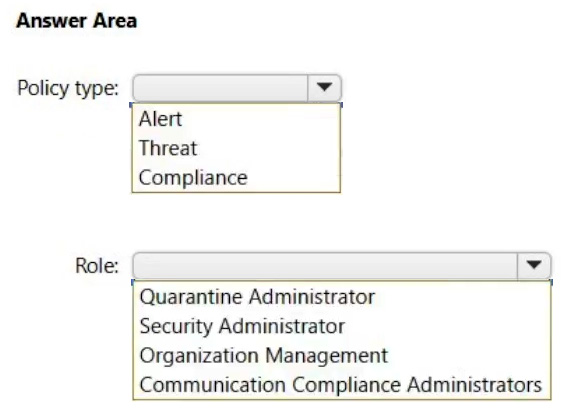
Correct answer:
Policy Type: Alert.
Alert policies notify administrators when specific conditions occur, such as malware detection, phishing attempts, or suspicious activities. This aligns perfectly with the need to notify admins about malware in emails.
Role: Security Administrator.
The Security Administrator role has permissions to configure security alerts, view security reports, and manage threat-related policies. This role is sufficient and adheres to the principle of least privilege.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/security/office-365-security/scc-permissions?view=o365-worldwide
QUESTION 20
You have a Microsoft 365 E5 subscription.
You need to compare the current Safe Links configuration to the Microsoft recommended configurations.
What should you use?
Correct answer: D
D. the Configuration Analyzer .
The Configuration Analyzer can help compare your current configurations against Microsoft's recommended configurations to ensure you are following best practices for security and compliance.
Although the Microsoft Secure Score can provide insights into your security posture and recommendations for improvement, the Configuration Analyzer is more aligned with comparing specific configurations against recommended settings.
Reference:
https://learn.microsoft.com/en-ie/microsoft-365/security/office-365-security/configuration-analyzer-for-security-policies?view=o365-worldwide
Choose MS-102 in Revizo and work through original, question-by-question practice on your iPhone. Review results, revisit what needs attention and keep your next session tied to one specific certification objective.
Practise MS-102 with RevizoNo. Revizo is an independent iPhone app for certification practice. Refer to the provider's official resources for current exam policies and registration.
Use the exam code to select the matching certification in Revizo, then build short, focused sessions around the areas you want to review.
No. Revizo provides original practice questions for certification study. Use the provider's official objectives, documentation and policies as the source of truth for your preparation.
Use the current Microsoft objectives, documentation and registration guidance as your source of truth. Revizo is designed to support focused practice, not replace the provider's official materials.
Check the official Microsoft exam page for the latest objectives, registration details and policies.